Red team vs penetration test is not a choice between a basic and a premium product. A penetration test finds and proves exploitable weaknesses in assets you name. A red team tests whether your people, detection and response can stop an adversary chasing a business objective. It pays off only once you have telemetry and a response path worth testing, and it generally does not replace the pentest your PCI DSS assessor expects.
The short answer
- A penetration test finds and proves exploitable weaknesses in named assets; a red team tests whether your detection and response stop an adversary pursuing a business goal.
- Buy a pentest for coverage, remediation evidence and compliance. Buy a red team only once logging, EDR, a monitoring team and an IR plan exist.
- Without those prerequisites, a red team mostly reports that nobody was watching, at several times the price of a pentest.
- Purple teaming and assumed breach assessments are the practical bridge between the two.
Key takeaways
- A pentest validates exploitable weaknesses in named assets; a red team tests whether detection and response stop an objective-driven adversary.
- A red team may use one quiet path and is not a comprehensive vulnerability discovery exercise.
- Without logging, EDR, a monitoring team and an IR plan, a red team mostly confirms that nobody is watching.
- A red team does not substitute for the PCI DSS v4.0 pentest and segmentation testing; DORA, TIBER-EU and CBEST are where red teaming is the mandated product.
- Purple teaming and assumed breach usually come before a full red team on the maturity ladder.
- Measure red teams by time to detect and respond, not by whether operators reached domain admin.
What is the difference between a red team and a penetration test?
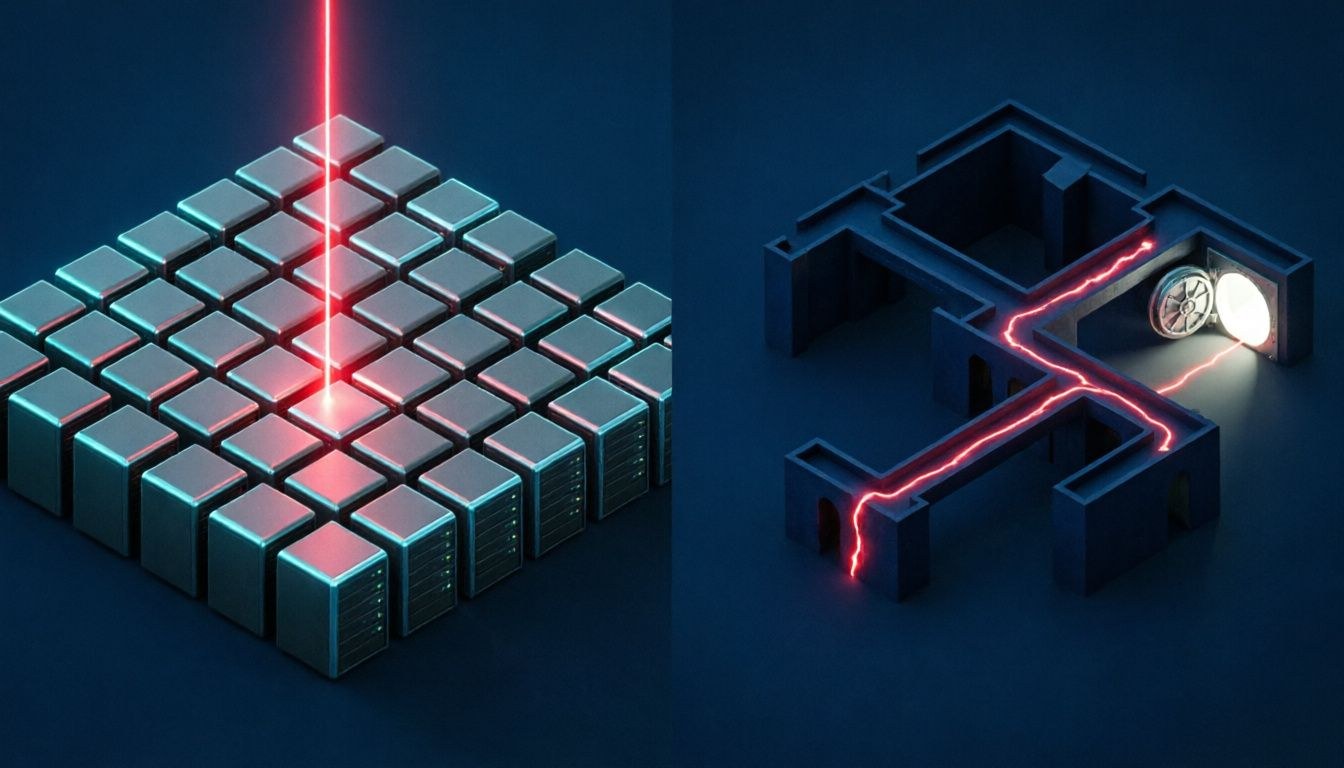
A penetration test answers “what can be broken in these assets, and how badly?” A red team answers “if a capable adversary went after this business objective, would we stop them, see them, or respond in time?” The first buys vulnerability coverage. The second buys a measurement of organizational resilience.
A pentest is scoped, time-boxed and asset-based: IP ranges, URLs, APIs, cloud accounts, repositories, test credentials and an exclusion list. Testers combine scanners, manual work and exploitation to surface as many validated weaknesses as the window allows, then rank them with evidence and remediation guidance. Widely used methodologies include NIST SP 800-115, PTES and the OWASP WSTG.
A red team is objective-based and organization-wide. The scope is a goal: read the customer database, reach domain admin, initiate a payment, exfiltrate a simulated dataset. Operators take whatever path a real adversary would, across people, process and technology, and report it as an attack narrative mapped to MITRE ATT&CK.
| Dimension | Penetration test | Red team |
|---|---|---|
| Question answered | What is exploitable in these assets? | Can we prevent, detect and respond to this adversary? |
| Scope | Assets: hosts, apps, APIs, cloud accounts | Objectives: crown-jewel data, privileged access, transactions |
| Typical duration | Days to a few weeks | Weeks to months |
| Stealth | Usually none; SOC often informed | Core requirement; only a white cell knows |
| Coverage | Breadth across the defined scope | One or a few viable attack paths |
| Detection testing | Only if explicitly scoped | Central to the engagement |
| Success metric | Validated findings, severity, coverage | Objective reached, time to detect, quality of response |
| Compliance role | Direct evidence for PCI DSS and audits | Supports assurance; mandated under TLPT regimes |
Stealth is how a red team operates, not what it delivers. Operators may exploit a single viable path and skip anything noisy, because every extra action raises the odds of detection without moving the objective forward. If an injectable parameter turns up on day two but a phished helpdesk account reaches the goal more quietly, the injection may never be fully tested.
That is why buying a red team to enumerate vulnerabilities is the most common procurement error here: you pay for depth on one path and get almost no breadth. The toolsets differ too. Pentests lean on Burp Suite, Nmap, Nuclei and Metasploit. Red teams add OSINT, phishing or vishing, C2 frameworks such as Cobalt Strike, Sliver or Mythic, and identity attack-path work with BloodHound.
A team that skips the threat intelligence phase and runs a generic playbook is not running a threat-led exercise, whatever the proposal calls it.
Does a penetration test test detection and response?
Not by default. Pentesters are noisy on purpose, their source IPs are often allowlisted, and the SOC is frequently told the test is happening. What your SIEM recorded during a standard pentest says little about how it would handle a real intrusion.
You can get detection data out of a pentest, but you have to scope it in:
- Require testers to keep a timestamped action log with source IPs, hosts and commands.
- Do not brief the monitoring team, or brief only a named escalation contact.
- After the test, reconcile the log against Splunk, Elastic Security or Microsoft Sentinel, and against EDR telemetry from CrowdStrike Falcon, SentinelOne or Microsoft Defender for Endpoint.
- Check cloud audit sources such as AWS CloudTrail and GuardDuty, Microsoft Defender for Cloud or Google Security Command Center.
All of this assumes telemetry: centralized logging, EDR on the endpoints in scope, identity logs, cloud audit logs and retention long enough to cover the engagement plus the investigation afterward. If retention is seven days and the test runs three weeks, the evidence is gone before anyone looks.
When is a red team premature for our organization?
When its most likely finding is something you already know. If critical known vulnerabilities are unpatched, logging is missing or short-lived, nobody monitors alerts, or IR contacts are stale, a red team will confirm all of that at several times the price of a pentest.
Without a SOC, an MDR provider or at least a working escalation path, the red team proves that nobody is watching. The result is accurate, predictable and hard to act on. A purple team or detection engineering sprint would have produced fixes instead.
Treat these as the minimum before commissioning a stealth red team:
- An asset inventory you trust, including cloud accounts and SaaS.
- A working patching and vulnerability management baseline, with prior pentest criticals closed.
- MFA on remote access and privileged accounts.
- Network segmentation around the systems that matter.
- Centralized logging with adequate retention, plus EDR coverage.
- A written incident response plan with current contacts.
- Executive sponsorship, legal rules of engagement and a deconfliction process.
If you cannot tick most of these, run pentests against the assets that carry the most risk, fix what they find and build telemetry first. The five-stage maturity ladder in the next section maps each stage to the engagement that fits it.
When is a penetration test no longer enough?
When it keeps answering a question you have already settled. The usual signals:
- Prior findings are remediated, and repeat tests return mostly low and informational issues.
- The board or a regulator wants end-to-end resilience assurance, not a vulnerability count.
- You have paid for a SOC, SIEM and EDR and need proof they catch realistic adversary behavior.
- A regulator mandates threat-led testing.
A clean pentest is also not proof of security. It means no exploitable issues were found in the scoped assets during that window. An adaptive adversary will go around them through identity, SaaS, CI/CD or a third-party integration.
The next step is rarely a full red team. Purple teaming is collaborative: operators run a technique, defenders check whether it fired, someone tunes a Sigma rule or EDR policy, and the technique runs again. Atomic Red Team and Caldera are common for structured execution. It fits when a stealth exercise would outrun the blue team’s ability to learn from it.
An assumed breach assessment skips initial access and starts from a foothold, typically a standard user workstation or a compromised VPN account. It tests internal detection, lateral movement, identity abuse and response. It suits organizations whose perimeter is reasonably mature and whose real question is blast radius.
| Maturity stage | What exists | Recommended engagement |
|---|---|---|
| 1. Foundations | Partial inventory, inconsistent patching | Vulnerability assessment, then focused pentests |
| 2. Hygiene | Inventory, patching cadence, MFA | Regular pentests of web, API, cloud and internal network |
| 3. Visibility | SIEM, EDR, cloud audit logs, retention | Pentests with detection reconciliation; purple team |
| 4. Response | SOC or MDR, IR plan exercised | Assumed breach; scoped red team |
| 5. Assurance | Detection engineering, threat intel program | Full-scope red team or TLPT (TIBER-EU, CBEST, DORA) |
Regulation sits at the top of the ladder. DORA requires threat-led penetration testing at least every three years for the EU financial entities that supervisors select, with TIBER-EU as the reference framework. In the UK, CBEST is the Bank of England’s intelligence-led testing framework. Both are red team exercises in practice: threat intelligence first, then objective-driven operations against live production.
If you might be in scope, read our DORA threat-led penetration testing page and confirm the criteria with your supervisor. Thresholds and timelines come from the regulators, not from a vendor.
How do duration, cost and compliance requirements compare?
A focused pentest of one application or network segment typically runs days to a few weeks; large cloud estates or multi-application scopes run longer. Red teams usually run weeks to months once you count threat intelligence, operations, reporting and retest.
The cost gap has specific causes. Stealth is slow, because operators throttle actions and wait. C2 servers, redirectors and aged domains must be built and maintained. Pretexts and physical work need legal review. A white cell and deconfliction calls consume senior time, and red team operators are usually a vendor’s most experienced people.
As a rough guide, focused pentests are often priced in the low-to-mid five figures in US dollars or euros, and red teams often cost several times more. Published ranges are unreliable, so get quotes against a written scope. Budget the retest separately in both cases.
Compliance is where the two stop being interchangeable. A red team that took one quiet path cannot show coverage of a cardholder data environment.
| Driver | What it expects | Does a red team satisfy it? |
|---|---|---|
| PCI DSS v4.0 | Internal and external pentests plus segmentation testing at defined intervals, commonly annually and after significant change | Not as a substitute; confirm with your QSA |
| ISO/IEC 27001:2022 | No fixed pentest cadence; technical vulnerability management controls apply | Can support conformity alongside pentest evidence |
| SOC 2 | No prescribed frequency; auditors may request security testing and remediation evidence | Possibly, depending on auditor and criteria |
| DORA, TIBER-EU, CBEST | Threat-led, intelligence-driven testing of live critical functions | Yes; this is the red team use case |
Two adjacent products also fail as substitutes. A vulnerability assessment prioritizes weaknesses, usually from scans, without validating exploitation. A bug bounty is continuous and incentive-driven, but coverage follows researcher interest, and it is generally not accepted as compliance evidence.
How do we measure a red team, and what must the rules of engagement cover?
Not by whether operators reached domain admin. A red team that reaches its objective but is detected and contained in forty minutes is a good result for the defenders. One that misses the objective but goes unseen for three weeks is a bad one.
Track these metrics with the same definitions across engagements so you can see change:
- Objective completion, and which path worked.
- Time to initial access and total dwell time.
- Mean time to detect, acknowledge and respond.
- ATT&CK techniques executed versus techniques detected.
- Alert fidelity: how many alerts fired, and how many were triaged correctly.
- Remediation closure rate at the retest.
The report should carry an attack timeline, ATT&CK-mapped TTPs, evidence, missed detection opportunities and business impact. Remediation spans detection engineering, IAM, segmentation and IR playbooks, owned by different teams. Unfunded remediation turns an expensive report into shelfware.
Rules of engagement come first for both products: written authorization from someone with authority over every in-scope asset, signed before any traffic is sent. They should name:
- The contracting entity and named signatories.
- In-scope and out-of-scope assets, including SaaS and third-party systems.
- Test windows, rate limits and data handling rules.
- An emergency stop procedure and communication channels.
- Deconfliction steps, so a real incident is never mistaken for the exercise, or the reverse.
Red teams add a white cell: trusted agents who track operator activity, manage safety and keep the blue team from escalating the exercise to law enforcement or the board. Without one, a stealth test can end in a real incident declaration.
Owning an application does not authorize testing the platform under it. AWS, Microsoft Azure and Google Cloud publish penetration testing policies; check the current text before scoping. Social engineering and physical testing need HR, legal, privacy and facilities sign-off, and EU engagements may need GDPR processing terms.
Is AI-agent red teaming the same as an enterprise red team?
No. “LLM red teaming” usually means a specialized application security assessment of a model, prompt pipeline, RAG system or agent. It does not test your SOC, your staff or your badge readers.
Testers target direct and indirect prompt injection, sensitive information disclosure, insecure output handling, excessive agency, RAG poisoning and model supply chain. In Model Context Protocol (MCP) deployments they add tool poisoning, malicious tool descriptions, token handling and confused-deputy behavior.
Reference points include the OWASP Top 10 for LLM Applications, MITRE ATLAS and the NIST AI RMF. The taxonomy is still moving, so write the scope out explicitly instead of relying on a framework label. Our AI agent penetration test scope checklist covers what to include.
The two do intersect. An agent with tool access to email, tickets or cloud APIs is a plausible initial access or privilege escalation path in an enterprise red team. If you run agents in production, tell the red team they exist and state whether operators may target them.
FAQ
Which should we do first, a penetration test or a red team?
A penetration test, almost always. Fix what pentests find and build logging, EDR and incident response first. A red team before that point mostly confirms gaps you could have predicted.
What is the difference between assumed breach and a full red team?
Assumed breach starts from a provided foothold, such as a user workstation, and tests internal detection, lateral movement and response. A full red team also tests initial access through phishing, external exploitation or physical entry.
Is purple teaming better than red teaming?
It answers a different need. Purple teaming builds and tunes detections collaboratively, which suits teams still developing their SOC. Red teaming measures whether those detections hold up when defenders do not know the test is running.
Does a bug bounty replace a penetration test?
No. A bug bounty is continuous and incentive-driven with uneven coverage, and it is generally not accepted as compliance evidence for frameworks like PCI DSS.
How do we evaluate a red team or pentest vendor?
Ask for the methodology, a redacted sample report, references, insurance and the named team who will do the work. Certifications such as CREST, CHECK, OSCP and OSEP are useful signals but do not guarantee engagement quality.
Does prompt injection testing count as a red team?
Not in the enterprise sense. It is an application security assessment of an AI system and does not exercise your SOC, staff or physical controls.
agent::offense runs both: scoped pentests for coverage and objective-driven red team operations for organizations ready to test detection and response. If you are unsure which one you need, we will tell you before you sign.